News Date: 2026-09-11
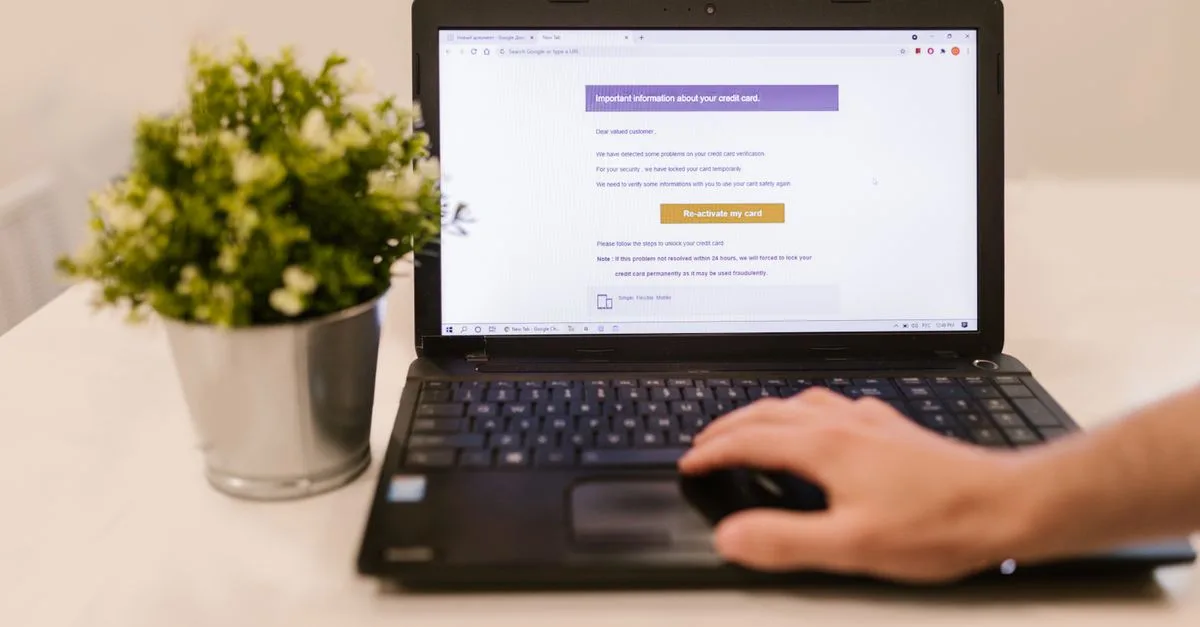
A security incident at marketing platform Brevo gave attackers access to a trusted communication channel used by hardware-wallet manufacturer Trezor. Rather than forging an ordinary sender address, the attackers distributed phishing messages through infrastructure associated with legitimate customer communications, making the campaign considerably more persuasive.
Trezor said the incident affected its opt-in newsletter database of roughly 347,000 email addresses. The fraudulent message claimed that a critical vulnerability in a wallet microcontroller placed customer funds at risk. Recipients were directed to download an application that requested their wallet backup, sometimes called a recovery seed.
Trust Was the Primary Target
The attackers did not need to compromise the hardware wallet itself. Their objective was to persuade users to surrender the secret that provides control over their cryptocurrency. Anyone obtaining a complete wallet backup can recreate the wallet and transfer its funds, potentially without any further access to the original device.
Trezor reported that the malicious domain was disabled within approximately 20 minutes. About 2,500 recipients had clicked the link before it stopped working. The company said its products, wallet systems and other internal services were not affected, but it is treating the newsletter addresses as potentially known to the attacker.
In my view, the most important lesson is that authentic delivery infrastructure does not guarantee authentic intent. Email security training often encourages users to inspect the sender, branding and writing quality. Those signals become far less useful when criminals operate through a compromised supplier account.
How Organizations Can Reduce the Risk
- Minimize the customer information stored in marketing platforms.
- Require phishing-resistant authentication for supplier administrators.
- Monitor for unusual campaigns, account changes and sending volumes.
- Establish emergency procedures for disabling links and outbound messaging.
- Use digitally verifiable notices for high-risk security communications.
- Regularly reassess vendors that can communicate directly with customers.
Users should never enter a wallet backup into a website or application reached through an unsolicited message. Anyone who disclosed a backup should create a new wallet and transfer the assets immediately. I believe companies handling financial technology must treat communications providers as part of their security perimeter because attackers increasingly target the relationship with customers rather than the core product.